IT Forensics & Incident Response
Quickly operational again, cleanly investigated
When an attack succeeds, two things matter: becoming operational again quickly – and understanding what actually happened. We deliver both. We secure evidence before it's lost, reconstruct the sequence of events step by step, and get your operations back up and running in a controlled way. For more than twenty years, the same question has driven us: how do you make an attack visible and understandable? What began as early research into visualizing attack data has become practical forensic work today – based on traceable method, not gut feeling.
When you need us
- Business Email Compromise / Payment Fraud: An invoice was paid to a changed bank account, or your supplier reports a payment you never made.
- Suspected compromised mailbox: Unexplained forwarding rules, unfamiliar logins, emails you never wrote.
- Ransomware or encryption: Systems are locked – you need to decide, act, and restart cleanly.
- Data exfiltration or suspected insider threat: There's a suspicion that data has left the building.
- Evidence preservation for legal action: You need forensically sound, resilient documentation for insurance, legal counsel, or court.
When in doubt: better to call once too early than once too late. The earlier we secure evidence, the more can be reconstructed.
Our Services
Incident Response – Immediate Measures
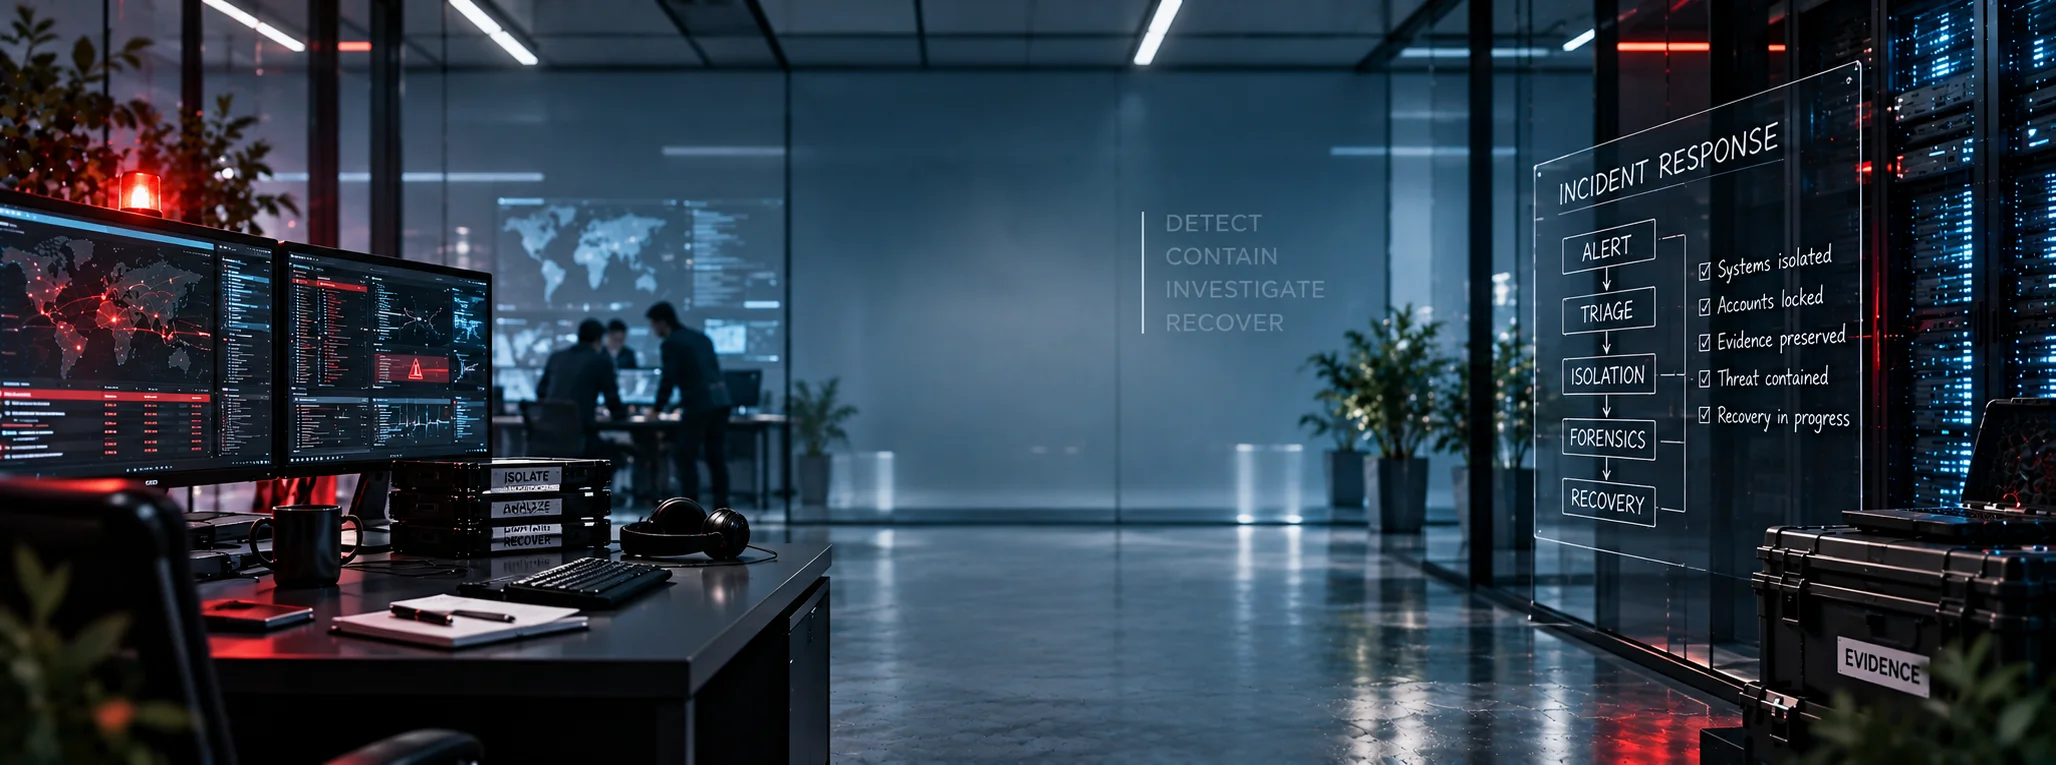
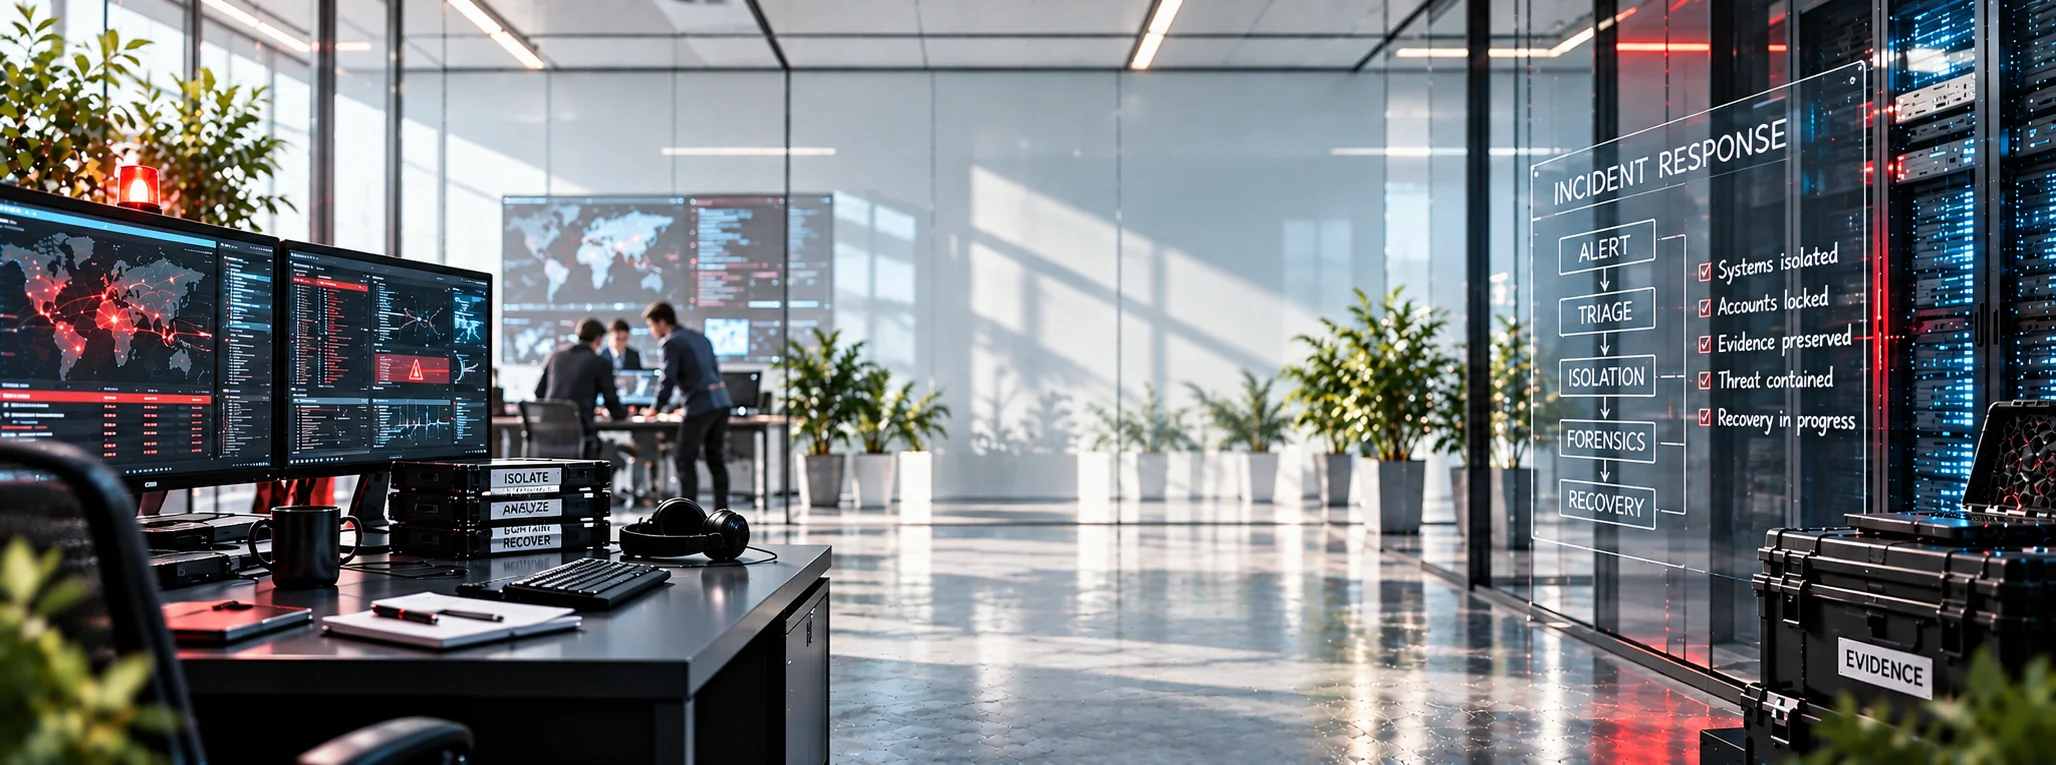
In an acute case, every hour counts. We help you contain the incident, isolate affected systems and accounts, and limit the damage – without prematurely destroying evidence. We then support a controlled restart.
Digital Forensics & Evidence Preservation
We secure data in a forensically sound manner, document everything completely, and maintain chain of custody, so our findings hold up with insurers, lawyers, and courts. You receive an understandable report – with a clear separation between established fact and reasoned assessment.
Investigating Email Fraud (Business Email Compromise)
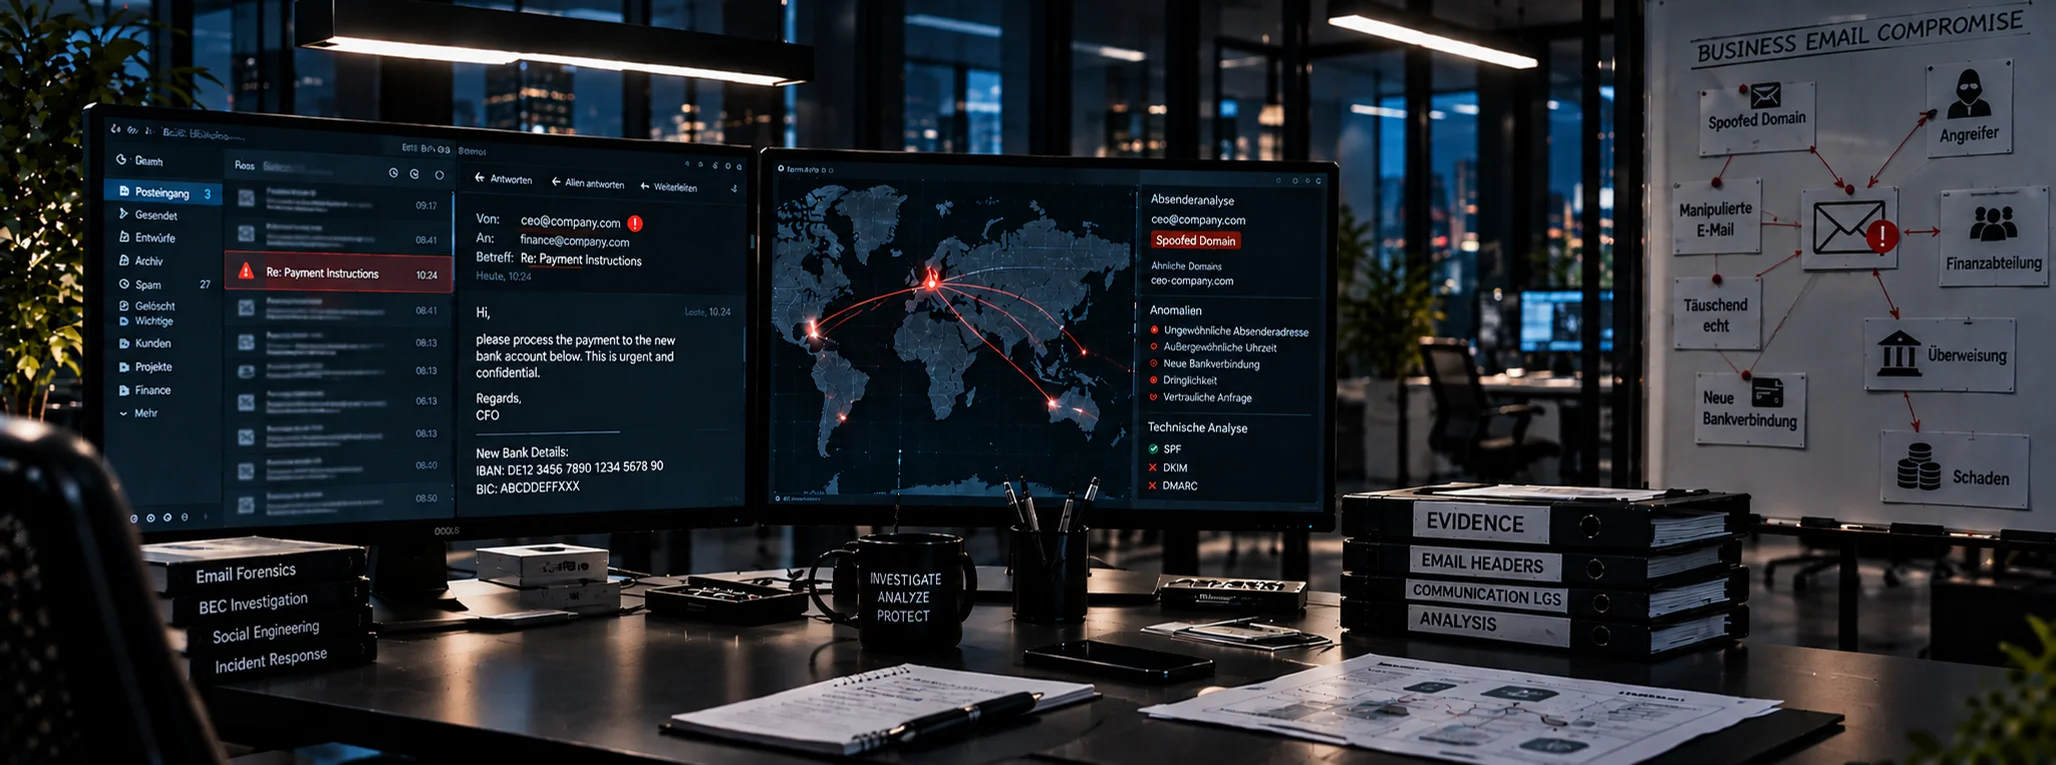
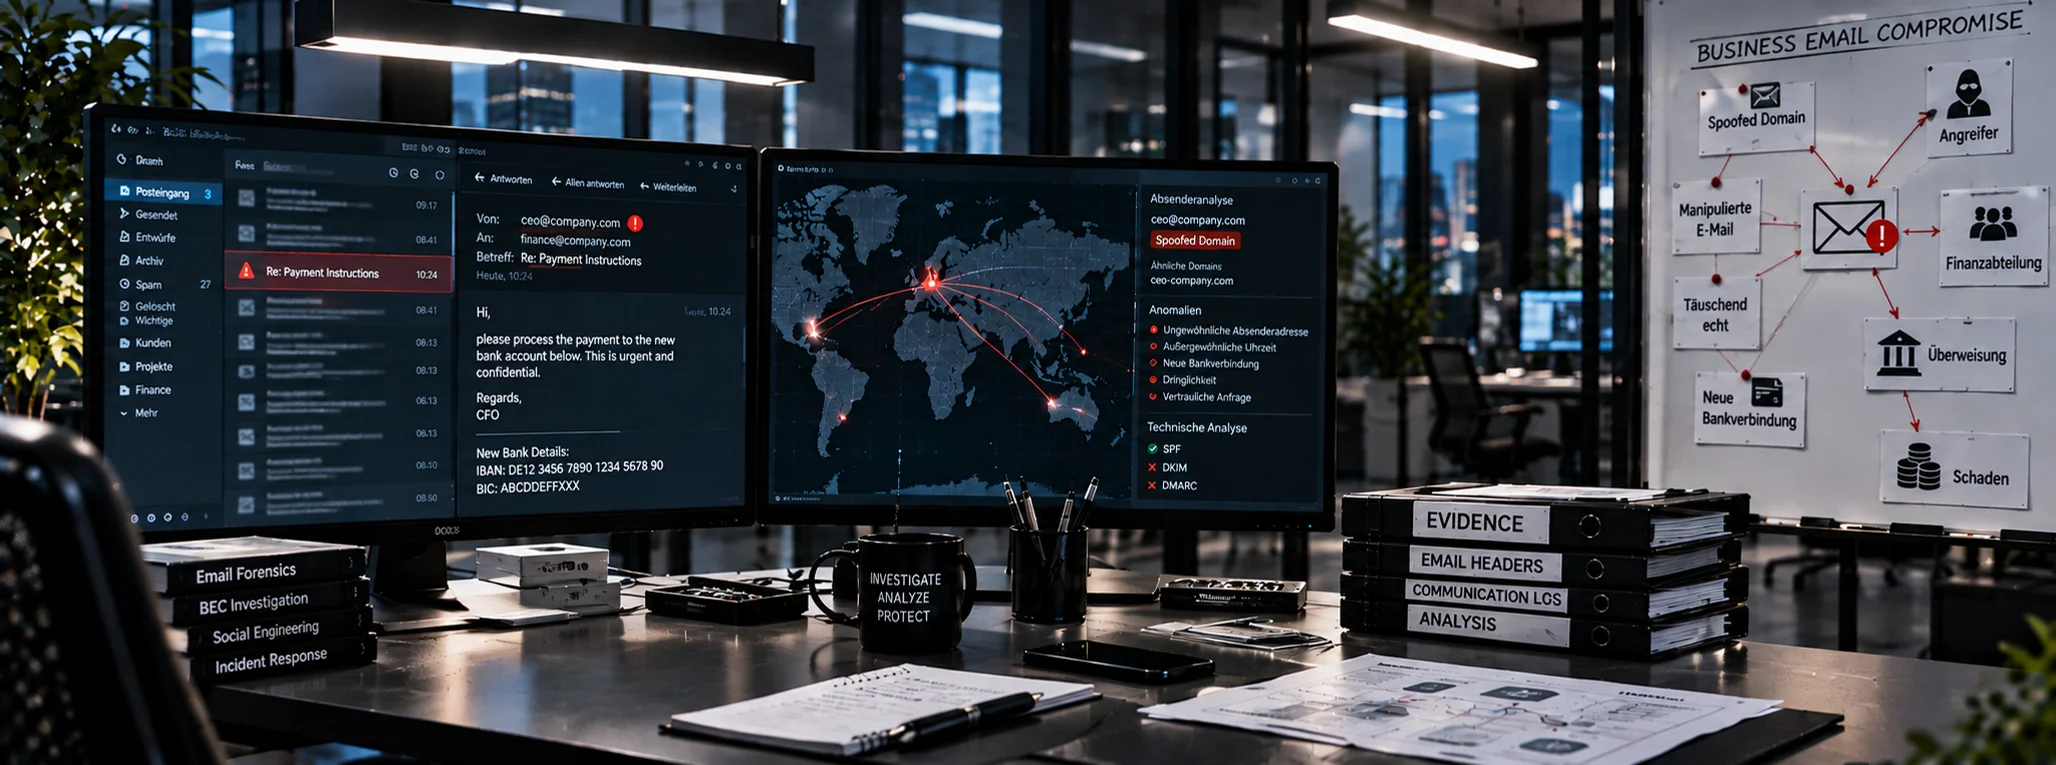
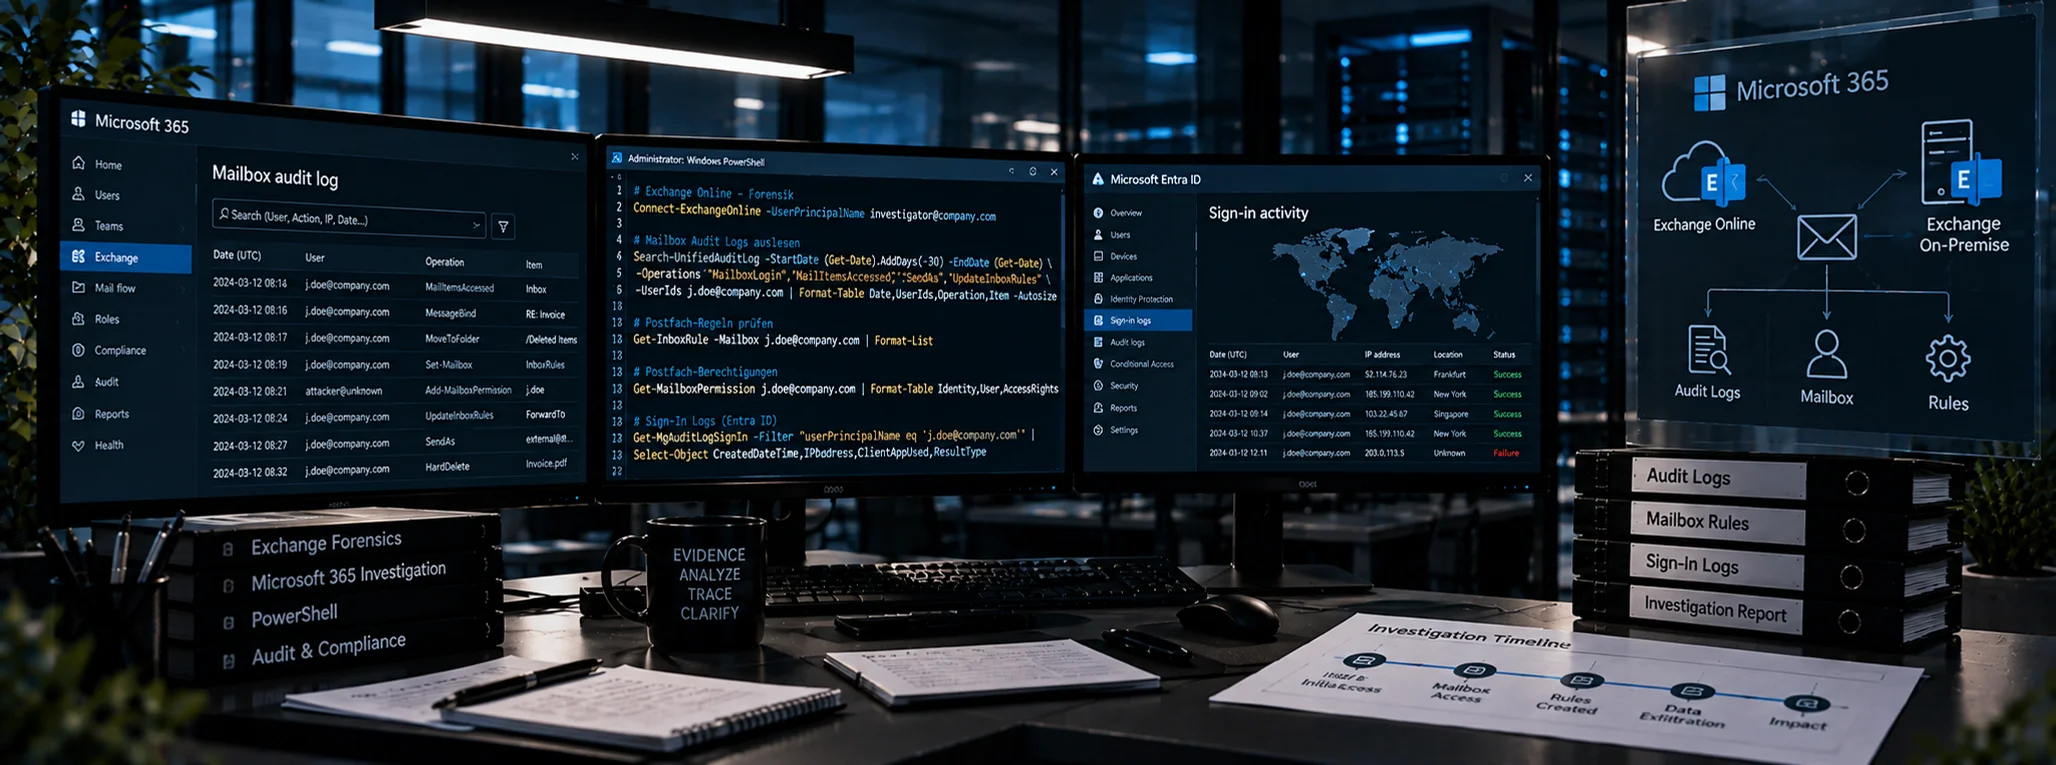
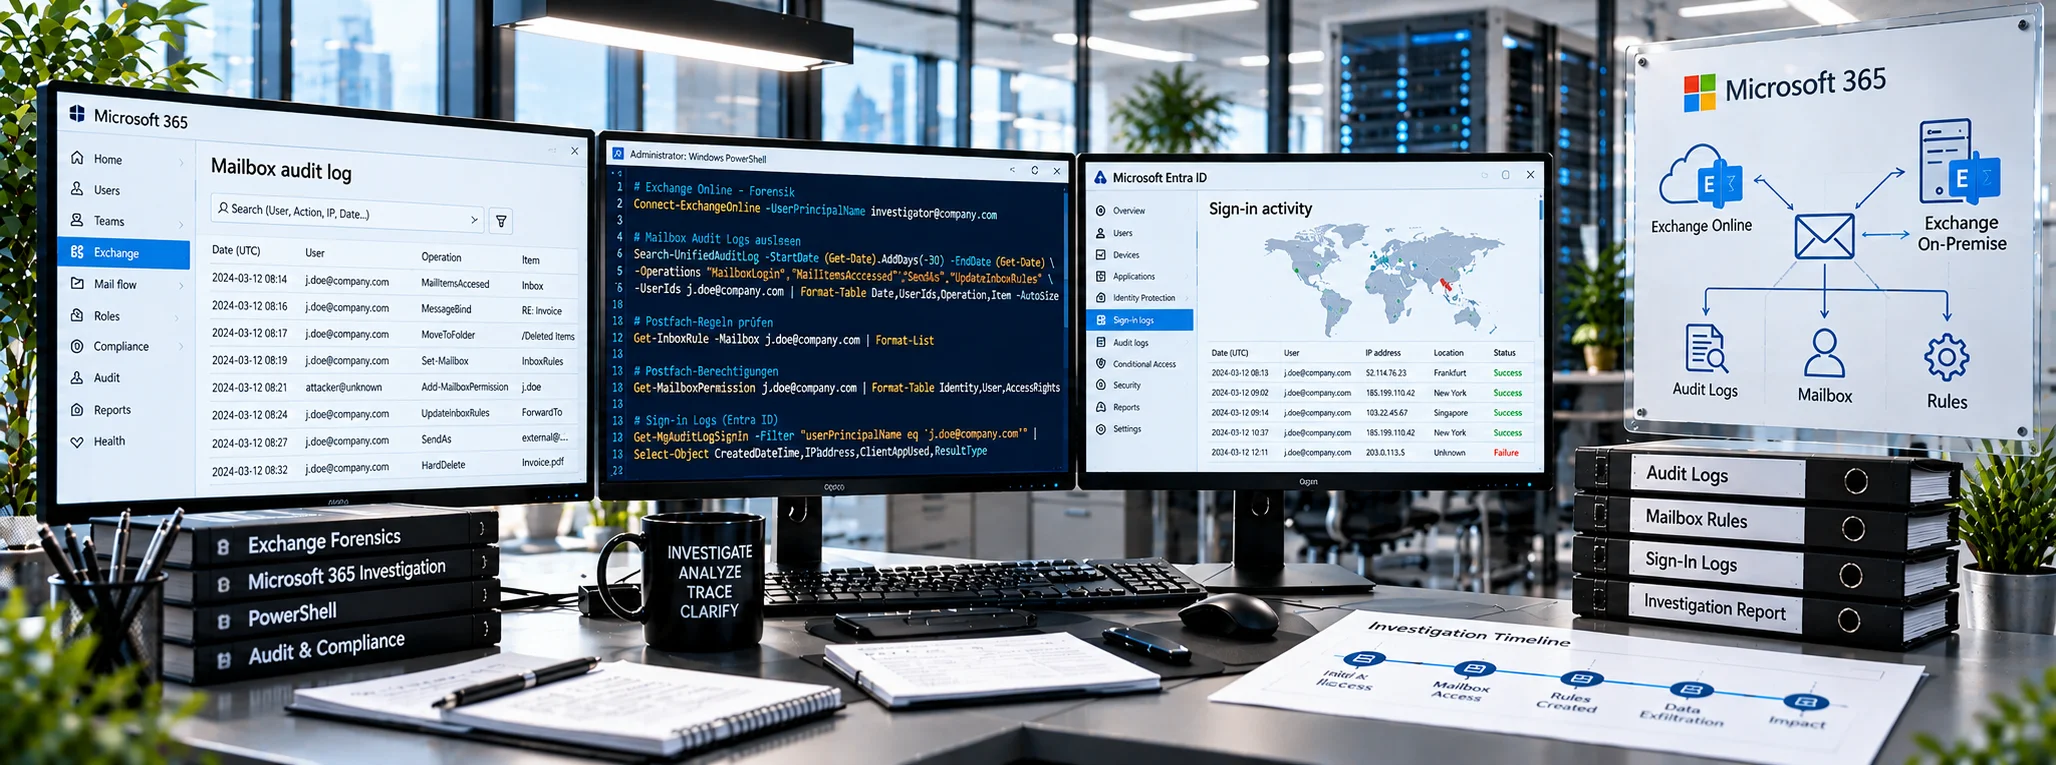
Our specialty. We reconstruct how attackers gained access, which look-alike or typo domains were used for communication, which forwarding and transport rules were set, and at what point a payment was redirected. Login and mailbox logs, geo/IP and timezone analysis together produce a solid picture – which we present as a timeline and communication pattern, so even non-technical people understand what happened.
Microsoft Exchange & Microsoft 365 Forensics
Whether Exchange Online or on-premise: we systematically evaluate login and mailbox audits, message histories, and rule sets – PowerShell-based and reproducible. This allows us to prove when and how a mailbox was taken over and what happened with it.
Hardening After the Incident
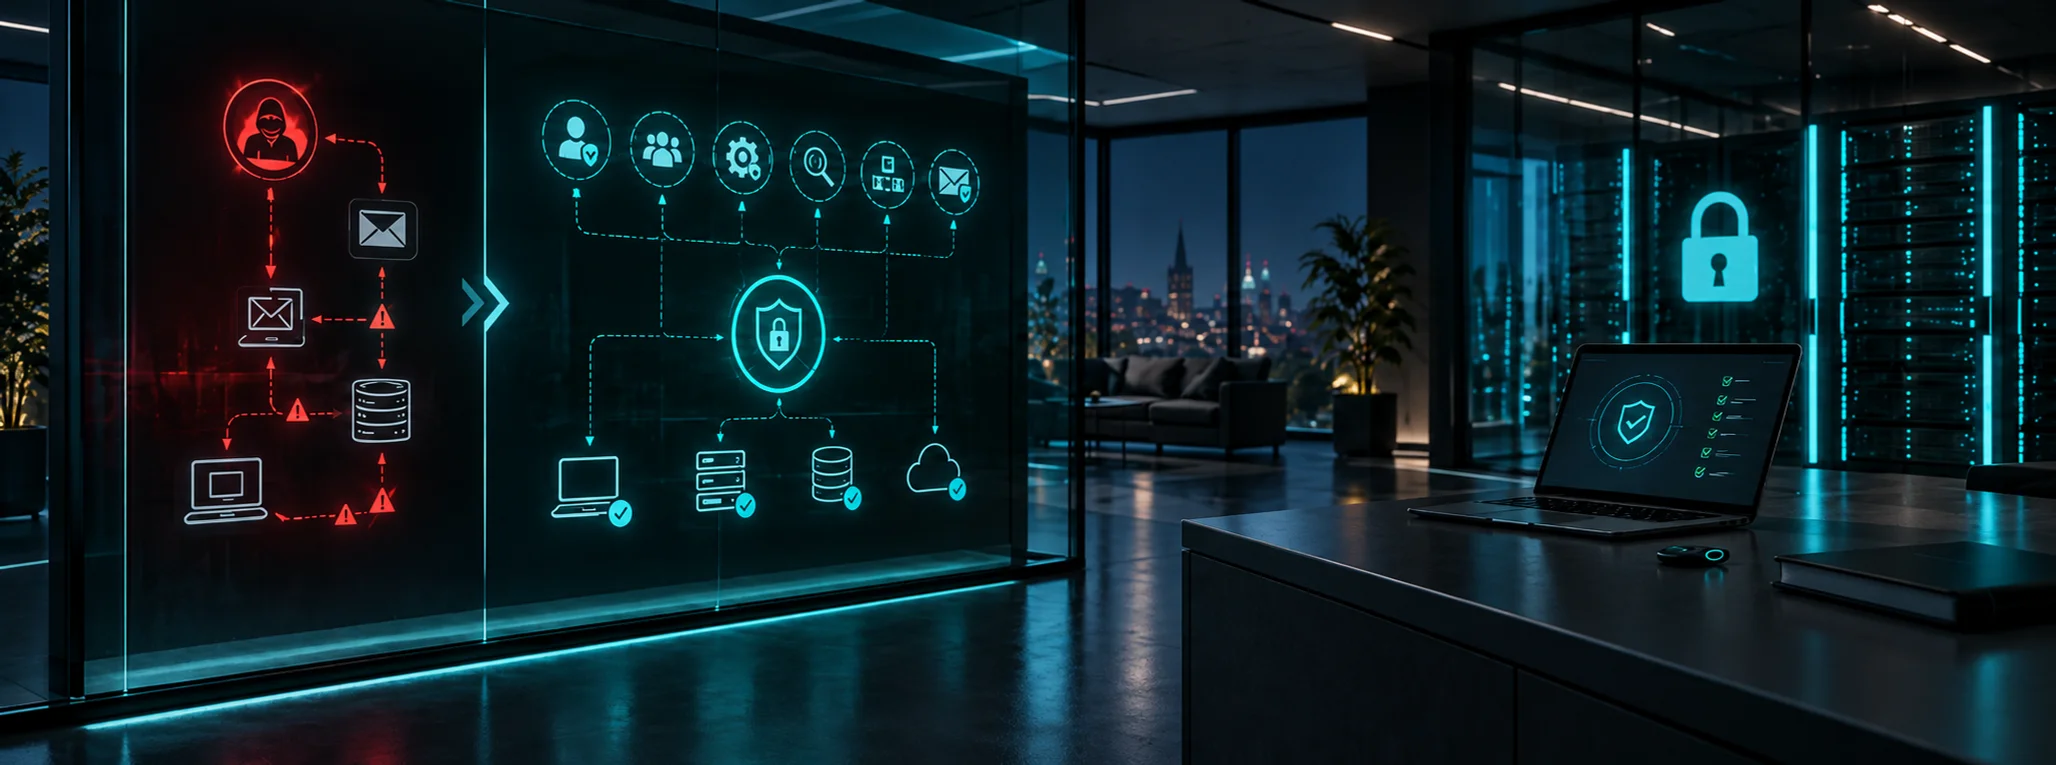
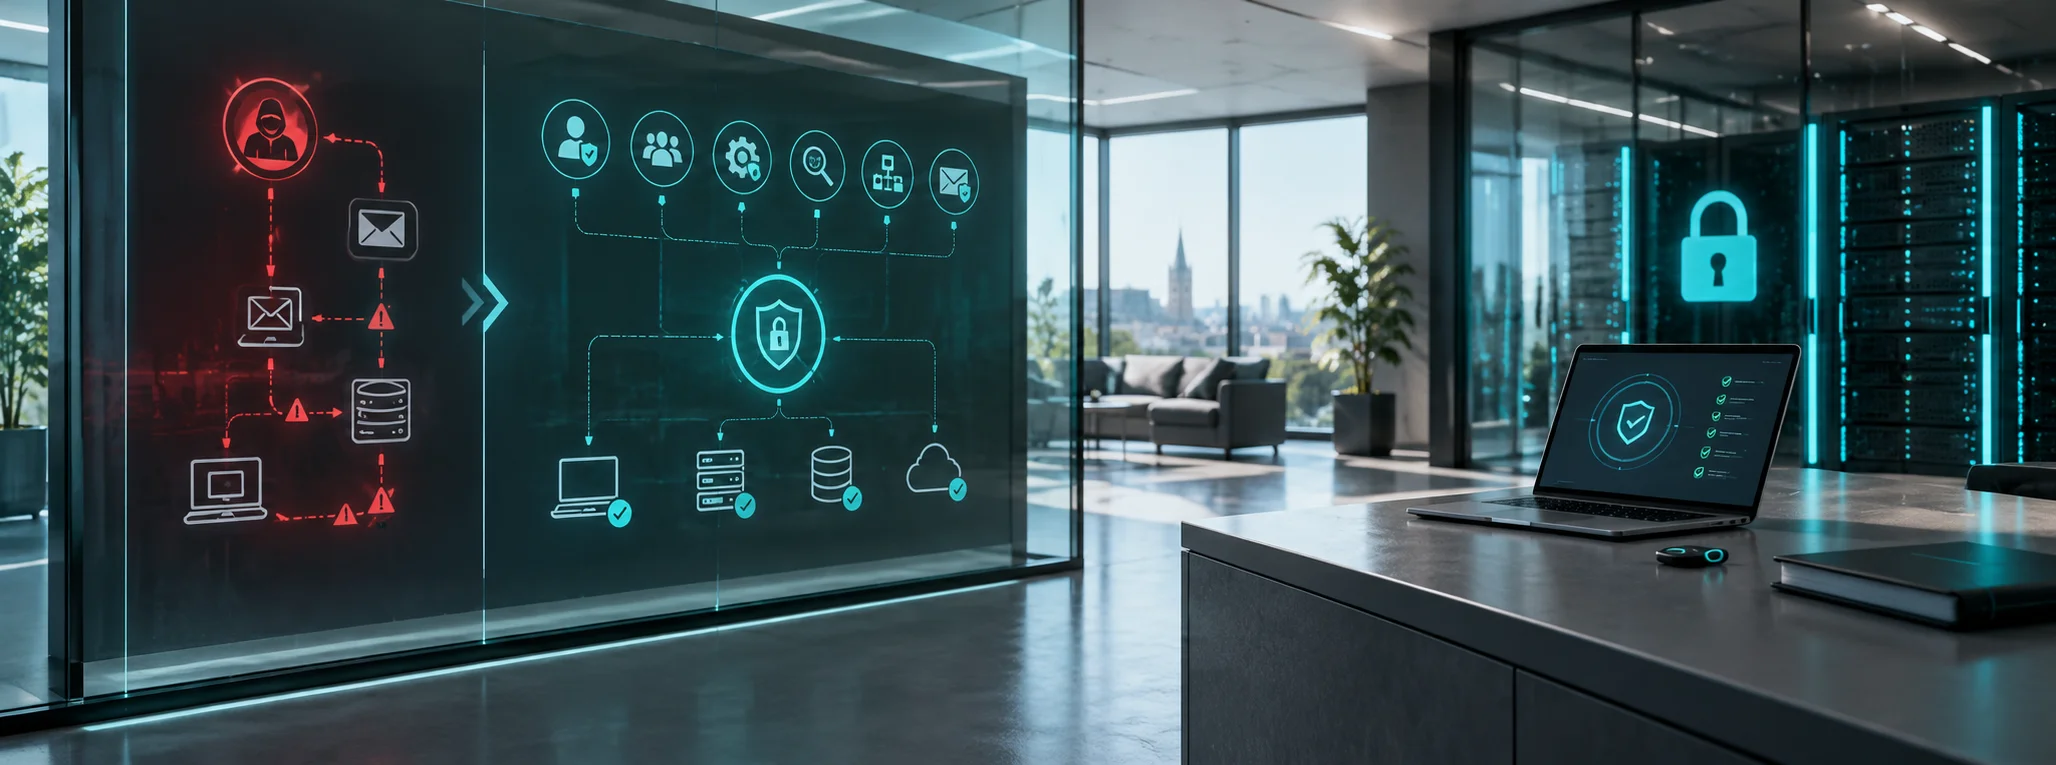
An incident isn't truly resolved until the entry point is closed. We derive concrete measures from our findings and harden your systems – so the same path can't be used a second time.
Training & Attack Demonstrations
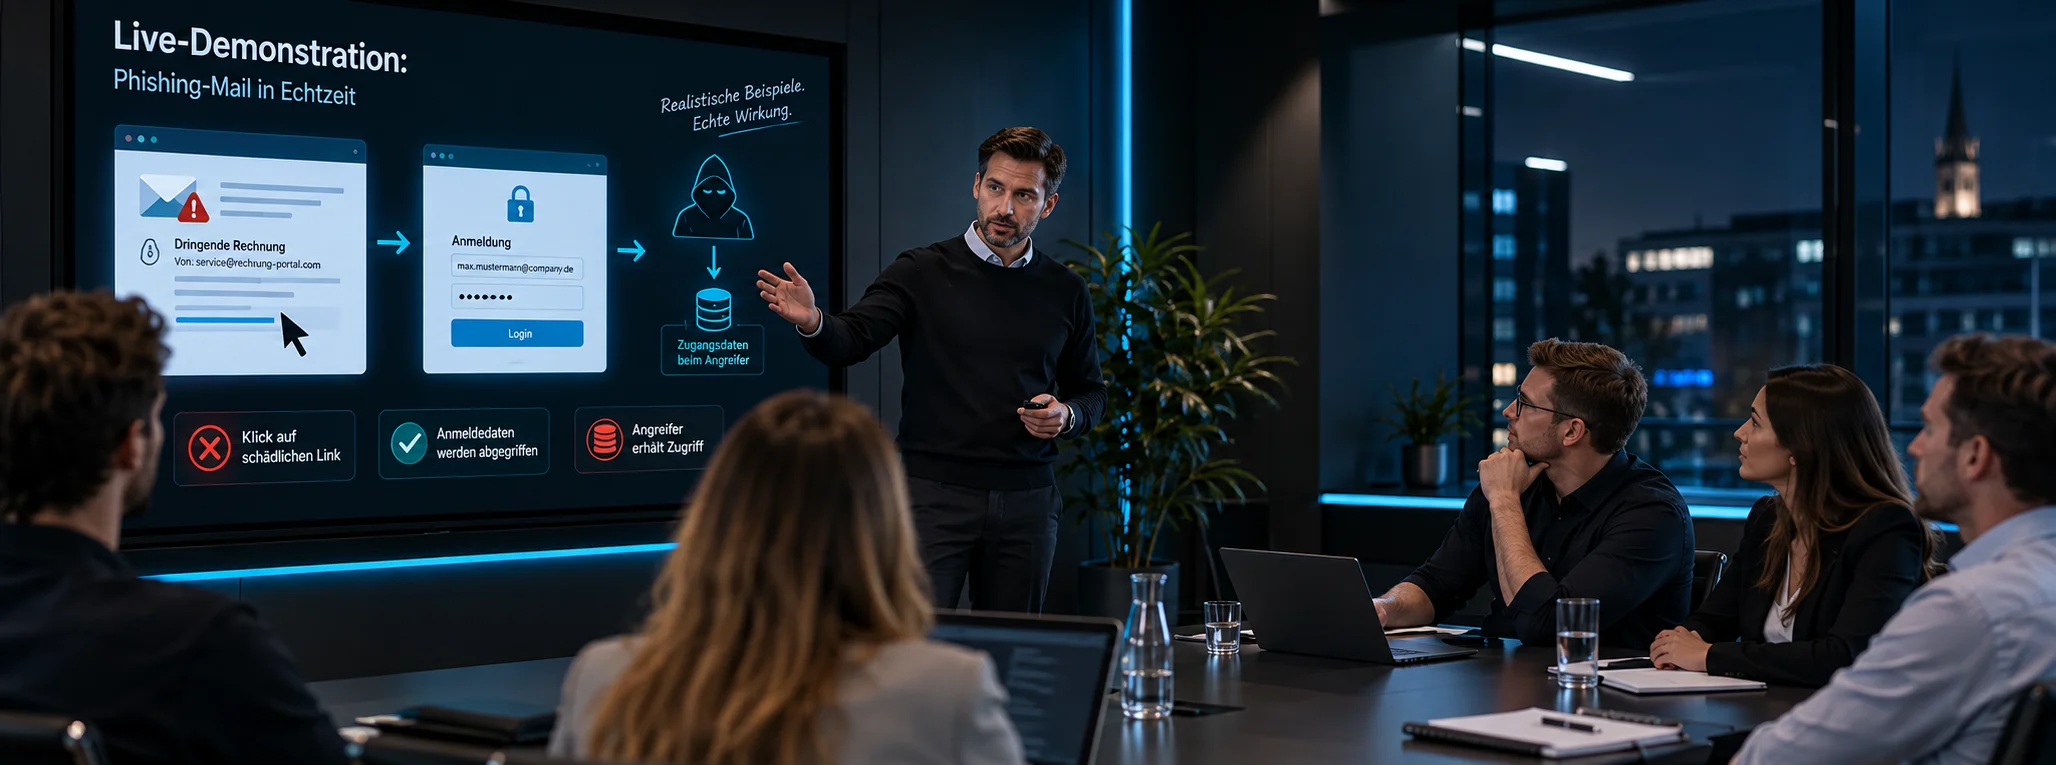
The most effective defense is an aware workforce. We demonstrate current attack techniques vividly and train your team using realistic examples – not abstract slides.
Discretion and Data Sovereignty
Security incidents are a matter of trust. We work confidentially, under NDA on request, and handle case data with the same sovereignty that shapes all our work: we process evidence and sensitive content on our own, controlled infrastructure – not in third-party clouds.
How a Collaboration Works
- Initial Contact & Situation Assessment – You describe the situation, we jointly decide the first, most urgent steps.
- Immediate Measures & Evidence Preservation – Contain the incident without destroying evidence.
- Analysis – Reconstructing the sequence of events from logs, mailboxes, and systems.
- Report – Traceable, with a clear factual basis and recommended actions.
- Hardening & Prevention – Closing the gap, preventing recurrence.
Suspect an active incident? Contact us directly.
The earlier we secure evidence, the more can be uncovered.
Emergency hotline: +49 621 715112